0
proof it’s yours
You built something great. But without a certificate, you’re asking them to trust you blindly. The agents that win come with proof.
Every agent you ship is a liability until it’s certified. AgentVerif scans, signs, and verifies LangChain agents automatically — so your buyers execute with confidence, not faith.
pip install agentverif-sign
You built something great. But without a certificate, you’re asking them to trust you blindly. The agents that win come with proof.
A single compromised agent wipes out user trust overnight. No patch fixes that. Certification is the only thing that proves you shipped clean.
Without activation limits, one buyer becomes a thousand. Pro licenses let you set exactly how many times your agent can be activated.
Three steps from source to certified. Fully automated, fully auditable.
agentverif runs a full OWASP LLM Top 10 scan on your agent ZIP. Score below 70? Refused. No exceptions.
score ≥ 70 requiredA cryptographic hash is generated. SIGNATURE.json is
injected. A License ID is issued. Your agent is certified.
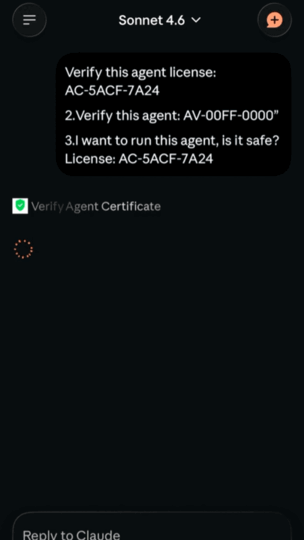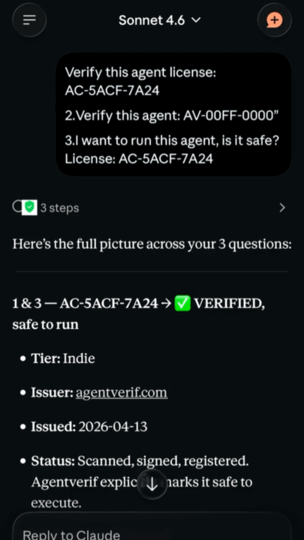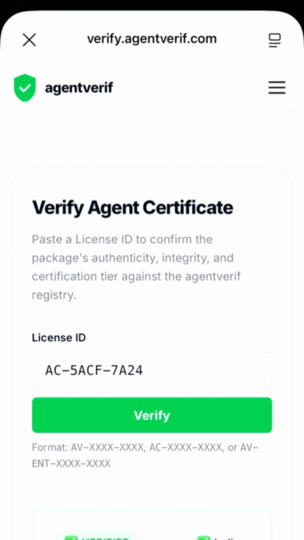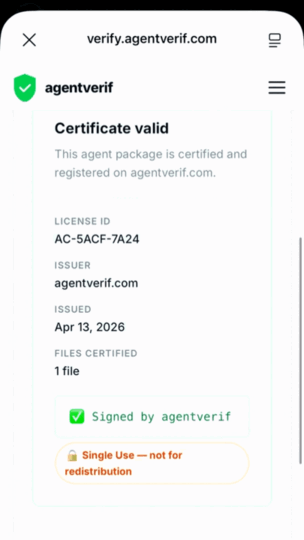
Buyers verify at verify.agentverif.com or via CLI. Tampered agents are flagged instantly. Claude blocks them automatically via MCP.
sha256 hash-lockedReal function names. No wrapper classes. Copy and run.
Sign your agent
from agentverif_sign.langchain_tool import sign_tool

# sign_tool is a LangChain StructuredTool
result = sign_tool.invoke({
    "zip_path": "./my-langchain-agent.zip"
})

print(result)
# ✅ SIGNED — agentverif certified
# License: AC-84F2-91AB
# Tier: indie
# Verify: https://verify.agentverif.com/?id=AC-84F2-91AB
Verify before executing
from agentverif_sign.langchain_tool import verify_tool

# verify_tool is a LangChain StructuredTool
result = verify_tool.invoke({
    "license_id": "AC-84F2-91AB"
})

print(result)
# ✅ VERIFIED — agentverif certified
# Tier: pro | ID: AC-84F2-91AB
# https://verify.agentverif.com/?id=AC-84F2-91AB
Full LangGraph pipeline
from agentverif_sign.langchain_tool import sign_tool, verify_tool
from langgraph.graph import StateGraph

# Add agentverif tools to your agent
tools = [sign_tool, verify_tool]

# Your agent now certifies before shipping
# and verifies before executing — automatically
graph = StateGraph(...)
graph.add_node("certify", sign_tool)
graph.add_node("verify", verify_tool)
Read the real implementation → src/agentverif_sign/langchain_tool.py
Every fork becomes a distribution point.
Every contributor ships verified agents by default.
Add this workflow and your repo becomes a node in the
AgentVerif network.
The standard spreads itself.
name: agentverif
on: [push, pull_request]
jobs:
  certify:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - name: Scan + Sign agent
        uses: trusthandoff/agentverif@v1
        with:
          mode: sign
          agent_zip: ./agent.zip
          tier: indie
      - name: Verify before deploy
        uses: trusthandoff/agentverif@v1
        with:
          mode: verify
          agent_zip: ./agent.zip
          fail_on_unsigned: "true"
The devs who certify first own the trust signal.
Late adopters play catch-up forever.
Founding spots available. First 100 get Pro free.
Signed yours? Open an issue titled “First 100: [Your License ID]” — we feature you on the leaderboard and amplify in communities.